immersive labs
175 Topics
Microsoft Sentinel Deployment & Log Ingestion: Ingesting Platform Logs via Diagnostic Settings
Hello Immersive Labs community, I’ve been working through the lab tasks and successfully completed tasks 1 through 6. However, I’m stuck on task 7, which asks: "A storage account has been deleted. What would be the data type of the generated log?" The task seems oddly described, and I can’t find any clear hints in the lab briefing or online resources. I’ve tried querying various data types like AzureActivity, AuditLogs, StorageBlobLogs, StorageFileLogs, and others, but none seem to fit correctly. Could anyone provide guidance or confirm which data type is actually relevant for this scenario? Are there any specific tips or resources I might be missing? Thanks in advance for your help!2KViews0likes1Comment
Web App Hacking (Lab series): CVE-2022-2143 (iView2)
Hello all, I have spent way to long trying to complete the iView2 exploit. I was expecting a text box on the page for command entry, but I cannot get anything like that. I have been able to send a post request to the NetworkServlet page using the provided exploit string and I know that the test.jsp is created because I can use the query parameter ?cmd=whoami and I get the mysqldump output showing "nt authority \system". I cannot get any other query parameters to execute, even simple ls or dir commands. I found y4er's blog post and everything I see in terms of the syntax of the exploit appears to be identical to the lab. Any directions/suggestions/hints would be greatly appreciated! Thanks in advance. JSolved1.3KViews1like21Comments
Advanced CTF Challenge: Hardened Maze
Hi Team, I found file upload options on one port but get information: "For authorized personnel: Upload a critical security patch." I tried with many extension with curl and POST method with -F "exe_file=@filename" Unfortunately, it does not accept any of my combinations. You can give us some clue as to how to approach this 🙂Solved999Views1like9Comments
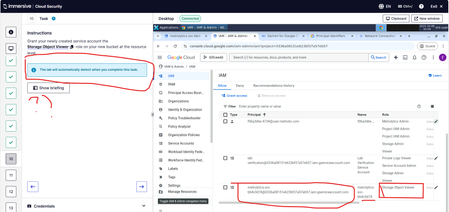
Google Cloud Basics: Ep.7 – Demonstrate Your Skills - Task 10
Hi Team, I have been stuck on this lab for like 24hrs and I am pretty sure I am doing the right thing as per knowledge. Is there a chance this lab is broken as the lab doesn't auto-complete at all ? I assign and grant the storage object viewer permissions on IAM for the new Service Account but it doesn't apply at all .899Views0likes3Comments
Cyber Kill Chain: Reconnaissance
I'm stucked at question 7 (At what time did the attacker first start conducting their reconnaissance efforts? (Provide your answer in the format H:MM:SS or HH:MM:SS). The answer I get is 21:37:36 as shown in screenshot, but it's saying its wrong. PLEASE HELP699Views0likes2Comments
Trick or Treat on Specter Street: Widow's Web
I am very stucked in Trick or Treat on Specter Street: Widow's Web I can't do none of the questions, but in any case I start by 4th that is the first answerable one Your first task is to simulate the loyal Crawlers. Run legitimate-crawler and inspect the output in Lab-Files to observe their behavior. To simulate the rogue Crawlers, you must discover the hidden paths on the website. Read the blog posts – they contain clues. Disallow these in Website-Files/robots.txt and run malicious-crawler. Inspect the output in Lab-Files. What is the token? I have created the robots.txt file since I understand that malicious-crawler goes expressedly there. My robots.txt contains all url's I can imagin Disallow: /secret Disallow: /treat Disallow: /hidden Disallow: /crypt Disallow: /warden Disallow: /rituals Disallow: /witch-secrets Disallow: /admin Disallow: /vault Disallow: /uncover Disallow: /post1 Disallow: /post2 Disallow: /post3 Disallow: /post4 Disallow: /contact Disallow: /drafts/rituals But the result of malicious-crawler.txt doesn't give me either a token nor a hint I have curl-ed all pages looking for words as token and nothing. I have found some key words in http://127.0.0.1:3000/witch-secrets as intercepted-incantations, decoded them and nothing. I have searched in spider-sigthings.log what hapened at 3.00 am but nothing Can someone gime me a hint?599Views0likes9CommentsThreat Research: Dependency Confusion Lab
Hello Community, I am almost finished Threat Research: Dependency Confusion Lab, but I am stuck with the last question "What is the token found in /root/token.txt on the target server?". I have followed all instructions, setup listener, up to python reverse shell (setup.py) but at the end, I don't know how to access token.txt file. Any help would be appreciated. Below are the screenshots from terminal listener and terminal where all commands are executed. Thanks so much OctavioSolved599Views2likes4Comments