help & support
325 Topics
Abusing Trust Boundaries for RCE
I'm a bit stuck on this one as I'm not that familiar with Git and all the associated terminology. How do I clone the repo? which dir does the .mcp.json file sit in? Does this not pre-exist as its adding extra capabilities\extension to the original code? Does the target host pull the file automatically to give me a shell? Many thanks - Gus13Views0likes0Comments
IOCs and TTPs extracting and identifying. Malware tab issue
For the IOCs and TTPs: Extracting and Identifying lab its asking me to get to the malware tab and it looks like theres suppose to be a scroll wheel to get to the malware tab but its not working at all, it may not be that but it only shows up when I get to that part and its unresponsive. Not sure where to go from here I've tried refreshing, clicking inside the panel, zooming in and out, using ai, looking online and none of it has worked. Before I get to the steps as you can see no scroll wheel under credentials tab. Now that I'm in the questions it shows what looks like a scroll wheel under the credentials tab: Anyone that can help please do, thanks.10Views0likes0Comments
Struggling to find the IT email on Simulations: BarterTown Delivery
During the last few days, I’ve been stuck on this lab, and I’m not sure what I’m missing. The lab asks us to use OSINT tools and techniques to gather intelligence about individuals to target within the organization, with the goal of testing the awareness of BarterTown’s IT staff and eventually gaining a foothold in the internal network. I’ve been using the information provided by the lab as a starting point for my reconnaissance. The website gives us several employees and their email addresses, but none of them are identified as IT staff. I also found the DNS SOA contact (hostmaster.bartertown.bitnet), but that appears to be a standard administrative DNS alias rather than an actual employee. The mail server does not seem to allow useful anonymous user enumeration, and the other reconnaissance results have not revealed the missing user. Has anyone completed this lab and can give me a hint about where/how the missing target information is supposed to be discovered?29Views0likes0Comments
Elastic Data Ingest: Demonstrate Your Skills Q9
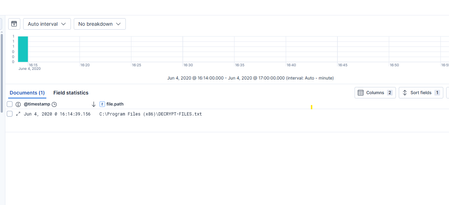
I have found the answers to all the other questions including 10 but I don't quite understand what Q9 is asking for when it says "Shortly after this file was created, two temp files were also created. What is the last 6 characters in the name of these temp files?" . I have found the files created after q8 answer see below but as far as I can see no combination of the perfstringbackup.tmp file is being accepted (have tried including the file extension and not) . Any guidance on what the question is actually looking for here ?130Views0likes3CommentsBrute Force task in an 15 min lab taking over 30 hours to complete
Hello everyone, I am doing an Immersive Labs about hacking, and there is a lab where I can learn how to crack codes with Hydra using SSH, HTTP, and FTP. The problem is that for the FTP part, I am supposed to brute-force a password (a 4-character password composed of lowercase letters and numbers). I am using the correct command, but the brute force is extremely slow, doing roughly 1 attempt every 3.5 seconds, which brings the total cracking time to over 30 hours. I waited 2 hours already, which is far too long, especially since the lab has to be extended every 10–15 minutes. However, now it has become personal, and I really want to get this password. Can anyone help? I am using the following command: hydra -l jimmy -x 4:4:1a -f -t 64 ftp://(ip address) i have tried -t, 4, 8 and 16, doesn't change anything I also tried creating 4 lists containing all possible passwords and running them in parallel with -P instead of using -x, but I always got too many attempts. Name of the lab ist: Credential Access: Using Hydra56Views0likes1Comment
DFIR CTF: LightNeuron DLL - Question 8
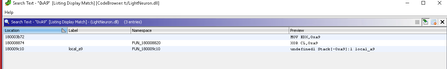
In relation towards finding the decrypted email. I am wondering about what I am getting wrong from the conditional breakpoint in order to expose all the decrypted strings after the return function After searching up the XOR key location I went to from Ghidra Through the RET function which I thought would expose the strings I ran going to the ret function then after following the process in order to go to the DLL malware and got into the ret function I set the breakpoint and debug restarted However, it kept saying memory address unavailable. such as this also includes setting the CF flag to 0 I am wondering about what I am doing wrong here and where should I dig deeper? Note: used Gemini to help look into possible solutions however, refered to https://www.youtube.com/watch?v=Tc8Wl37uwYc for aid49Views0likes1CommentHelp with Cross Site Request Forgery (Twooter)
Hi folks, I'm having a hard time getting past the Cross Site Request Forgery lab - specifically I'm not sure what sort of payload I can use to obtain the username of the scraper. I can get their IP address using just a link and I've tried a range of scripts hosted on my machine which I then link to in my 'twoots' but there's no connection at all. I'd be really grateful for any direction as to the sort of payload that could capture the necessary information. Thanks, JonathanSolved490Views0likes6Comments
404 Oops. You look lost.
I am trying to complete a training: 2026 Application Developer IS Curriculum for Non-Employees-ASP.NET At step 4: 2026 Application Developer IS Curriculum for Non-Employees-ASP.NET directs me to the Immersive Lab page, but I get this message: I tried to contact the support team, but it sends me to this page and when I click to log in, it comes back here, it's a loop: If I try to access the page where I should have the task assignments, it is empty. What could I do in this case? I am waiting for an answer.113Views0likes3Comments