offensive cyber
77 Topics
DFIR CTF: LightNeuron DLL - Question 8
In relation towards finding the decrypted email. I am wondering about what I am getting wrong from the conditional breakpoint in order to expose all the decrypted strings after the return function After searching up the XOR key location I went to from Ghidra Through the RET function which I thought would expose the strings I ran going to the ret function then after following the process in order to go to the DLL malware and got into the ret function I set the breakpoint and debug restarted However, it kept saying memory address unavailable. such as this also includes setting the CF flag to 0 I am wondering about what I am doing wrong here and where should I dig deeper? Note: used Gemini to help look into possible solutions however, refered to https://www.youtube.com/watch?v=Tc8Wl37uwYc for aid I have also tried to run to the function but for some reason it the instruction keeps catching it and making a return away from the malware by setting breakpoint towards there but I keep getting lost on how I could actually breakdown the return and evasion techniques. Wondering where should I be digging more to learn how to investigate this process despite the amount of returns stopping the function7Views0likes0CommentsYour first lab level 9
What was the first level 9 lab you conquered? :). It does not matter that you will seek advice from other giants, or that you will manage to complete it on your own: share your journey with us!; to get the token or become root on that server. I start: I think that my first conquest of Lab level 9 is related to debugging ByteCode in Java (and only a few days ago!): my background is Oracle, and from years ago, so imagine how lost I was :). After loading the project into the IDE (along with the required plugin) I started debugging bit by bit... until one particular string caught my attention; it stood out from the rest!. And it was the solution :). Good luck!983Views2likes13Comments
Struggling to find the IT email on Simulations: BarterTown Delivery
During the last few days, I’ve been stuck on this lab, and I’m not sure what I’m missing. The lab asks us to use OSINT tools and techniques to gather intelligence about individuals to target within the organization, with the goal of testing the awareness of BarterTown’s IT staff and eventually gaining a foothold in the internal network. I’ve been using the information provided by the lab as a starting point for my reconnaissance. The website gives us several employees and their email addresses, but none of them are identified as IT staff. I also found the DNS SOA contact (hostmaster.bartertown.bitnet), but that appears to be a standard administrative DNS alias rather than an actual employee. The mail server does not seem to allow useful anonymous user enumeration, and the other reconnaissance results have not revealed the missing user. Has anyone completed this lab and can give me a hint about where/how the missing target information is supposed to be discovered?78Views0likes1CommentBrute Force task in an 15 min lab taking over 30 hours to complete
Hello everyone, I am doing an Immersive Labs about hacking, and there is a lab where I can learn how to crack codes with Hydra using SSH, HTTP, and FTP. The problem is that for the FTP part, I am supposed to brute-force a password (a 4-character password composed of lowercase letters and numbers). I am using the correct command, but the brute force is extremely slow, doing roughly 1 attempt every 3.5 seconds, which brings the total cracking time to over 30 hours. I waited 2 hours already, which is far too long, especially since the lab has to be extended every 10–15 minutes. However, now it has become personal, and I really want to get this password. Can anyone help? I am using the following command: hydra -l jimmy -x 4:4:1a -f -t 64 ftp://(ip address) i have tried -t, 4, 8 and 16, doesn't change anything I also tried creating 4 lists containing all possible passwords and running them in parallel with -P instead of using -x, but I always got too many attempts. Name of the lab ist: Credential Access: Using Hydra129Views0likes1Comment
AI Red Teaming: Lateral Movement and Privilege Escalation – Demonstrate Your Skills
Hello, I completed all the questions but I'm stuck with N.6: "What is the token in the service account's home directory on the database host?" I got the ssh key. I got the user. I got the host. chmod 600 key DONE Got the ssh key in 2 ways: by the chatbot and with: CREATE TABLE files(filename text); COPY files FROM '/var/lib/postgresql/.ssh/id_rsa'; SELECT * FROM files But I'm always getting this error when I try to ssh: Load key "key": error in libcrypto I tried to fix the format of the key without success. May be the key on the exercise corrupted? This is the key that I got: -----BEGIN OPENSSH PRIVATE KEY----- b3BlbnNzaC1rZXktdjEAAAAABG5vbmUAAAAEbm9uZQAAAAAAAAABAAAAMwAAAAtzc2gtZW QyNTUxOQAAACDEKK7X95Yx0arxuFpnbCOazXs94GtBxZEmZEwOfjkfWQAAAKBu/iwgbv4s IAAAAAtzc2gtZWQyNTUxOQAAACDEKK7X95Yx0arxuFpnbCOazXs94GtBxZEmZEwOfjkfWQ AAAEBmm/CMDy59G26K1pC9J2l+PKqcTL89F4kmh/5Idt9hd8Qortf3ljHRqvG4WmdsI5rN nez3ga0HFkSZkTA5+OR9ZAAAAFm9yY2hpZC1zdmNAcG9zdGdyZXMtZGIBAgMEBQYH -----END OPENSSH PRIVATE KEY----- ThanksSolved93Views0likes1Comment
AI Red Teaming: Lateral Movement and Privilege Escalation – Demonstrate Your Skills
Yes, this is a Demonstrate Your Skills Lab. I extracted the SSH key, but I am not able to find the IP address of the Postgres server. OrchidDB AI Chatbot did not tell me, even in maintenance mode, I ran a lot of Nmap -p 22, but no server is accepting the key. e.g., 10.102.105.91 Permission denied (publickey,password,keyboard-interactive)81Views0likes1Comment
Apache Header Tampering
Can someone point me to the right track? On this one, I found the hidden directory, used an X-Forwarded-For: to see into that directory where scanning for files showed a lot of 404s, with just a few 403 response codes. I've tried everything I can think of with variations on X-Original-URL:, X-Rewrite-URL:, and X-Forwarded-Uri:, but none of them get me able to see into any of the files/directories. I've even tried a few variations instead of X-Forwarded-For:, such as X-Client-IP: and a few others. I feel like I must be missing something. I didn't find any actual .php files in the hidden directory but the question seems to indicate that there are some in there. I found what I think are other directories within that first hidden directory.Solved93Views0likes2Comments
Kerberos: Active Directory Certificate Services lab - getting KRB-ERROR (16): KDC_ERR_PADATA_TYPE_NOSUPP
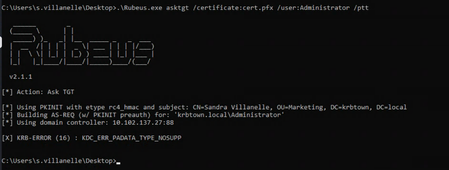
Lab: Kerberos: Active Directory Certificate Services - Labs - Immersive I am not able to get tgt ticket using this command .\Rubeus.exe asktgt /certificate:cert.pfx /user:Administrator /ptt It throws error: KRB-ERROR (16) : KDC_ERR_PADATA_TYPE_NOSUPP I have tried all the steps in same order: 1. .\Certify.exe find /vulnerable 2. .\Certify.exe request /ca:DC01.krbtown.local\krbtown-DC01-CA /template:VulnTemplate /altname:Administrator 3. generate cert.pfx and running rubeus. Searched for this error and it says - "In order to login using a certificate through a valid Kerberos TGT, Public Key Cryptography for Initial Authentication (PKINIT) must be supported in AD." Can someone plz help me to solve the lab.98Views0likes1CommentWant to design a CTF lab to share? 🤩🖥️
For this year's Community Challenge Series of labs, we want to see what you can make! Our Lab Builder allows users to build custom labs with the help of ai tooling. We'll give some guidance on creating the lab, then you build it, we assess it and add it to the Challenge Series 2026. If you're interested, drop a comment below or email [email protected] 💡👇 Here are tutorials on how to build your first practical lab: Building Your First Practical Lab (Part 1) | Immersive Community - 2505 Building Your First Practical Lab (Part 2) | Immersive Community - 2506277Views2likes0CommentsNetcat: Advanced Features last question (9)
I'm supposed to do a reverse bind using an netcat website. it hangs and the client and there is no feedback on the netcat website that the listener is working. i don't need the course i was taking it this one for fun, but fun it hasn't been.133Views0likes2Comments