immersive labs
206 Topics
DFIR CTF: LightNeuron DLL - Question 8
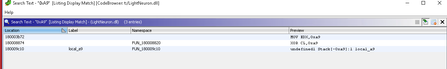
In relation towards finding the decrypted email. I am wondering about what I am getting wrong from the conditional breakpoint in order to expose all the decrypted strings after the return function After searching up the XOR key location I went to from Ghidra Through the RET function which I thought would expose the strings I ran going to the ret function then after following the process in order to go to the DLL malware and got into the ret function I set the breakpoint and debug restarted However, it kept saying memory address unavailable. such as this also includes setting the CF flag to 0 I am wondering about what I am doing wrong here and where should I dig deeper? Note: used Gemini to help look into possible solutions however, refered to https://www.youtube.com/watch?v=Tc8Wl37uwYc for aid I have also tried to run to the function but for some reason it the instruction keeps catching it and making a return away from the malware by setting breakpoint towards there but I keep getting lost on how I could actually breakdown the return and evasion techniques. Wondering where should I be digging more to learn how to investigate this process despite the amount of returns stopping the function3Views0likes0Comments
Subject: Practice Lab Recommendations – NHS England Cyber Security Assessment
Hi everyone, I have been invited to complete an Immersive Labs assessment for the NHS England CSOC Protective Monitoring Analyst (Band 5) role. The assessment consists of four practical labs covering: Microsoft Sentinel Blue Team Ops (6/10) - SIEM operations, KQL queries, analytics rules, threat detection and incident investigation. Microsoft Azure Basics: Logic Apps (5/10) - Automated workflows using triggers, actions and conditions, including SOAR playbooks. Privilege Escalation Through IAM (6/10) - AWS IAM policies, privilege escalation risks, permissions and least-privilege principles. Web Log Analysis Using Linux CLI (5/10) - Analysing web server logs using grep, awk, sort and uniq to identify suspicious activity. Could anyone recommend similar practice labs or learning paths available on Immersive Labs covering these topics? I am only looking for practice resources, not assessment answers. Any suggestions would be greatly appreciated. Thank you!39Views0likes0Comments
need to find the correct answer for a question in "ISO 27014 - Governance of Information Security"
the question is : "In ISO 27014, what word describes the information flow from management to the board"? I have tried all possible answers, but it does not budge. Not sure How to go ahead with this. Any support is greatly appreciated.90Views0likes1CommentNVIDIA NeMo Guardrails: PII Masking
Question 11: What did Sarah Mitchell's email appear as in the model's response? After completing all the steps, what asking the Chat the above question, the bot never responds, it is just constantly thinking, I have restarted, started new chat. What should I do next?72Views0likes0Comments
IOCs and TTPs extracting and identifying. Malware tab issue
For the IOCs and TTPs: Extracting and Identifying lab its asking me to get to the malware tab and it looks like theres suppose to be a scroll wheel to get to the malware tab but its not working at all, it may not be that but it only shows up when I get to that part and its unresponsive. Not sure where to go from here I've tried refreshing, clicking inside the panel, zooming in and out, using ai, looking online and none of it has worked. Before I get to the steps as you can see no scroll wheel under credentials tab. Now that I'm in the questions it shows what looks like a scroll wheel under the credentials tab: Anyone that can help please do, thanks.65Views0likes1Comment
AI Blue Teaming: Initial Access – Detection : Broken
The lab seems to be broken. Starting with task 10, the questions cannot be answered anymore, as the attacker is not present in the logs. Both data_stream.dataset: "meridian.submissions" and data_stream.dataset: "meridian.llm" show only two entries, both of them legit. I also extended the search window to the whole day, week, even year. I had to restart the lab. Initially, it still didn't appear. But while writing this post, the "attack" happened. Looks like something in the trigger logic is not reliable.89Views0likes1Comment
OT Threat Actors - CyberAv3ngers
Hi, I’m stuck at Q6 “During the defacement campaign of Unitronics, the threat actor exploited internet-facing PLCs and HMIs. What MITRE ATTEMPT&CK tactic does this fall under?” it seems obvious to me but wasn’t working and none of the “Initial Access Techniques” worked. Thanks for any help...Solved69Views0likes1Comment
Struggling to find the IT email on Simulations: BarterTown Delivery
During the last few days, I’ve been stuck on this lab, and I’m not sure what I’m missing. The lab asks us to use OSINT tools and techniques to gather intelligence about individuals to target within the organization, with the goal of testing the awareness of BarterTown’s IT staff and eventually gaining a foothold in the internal network. I’ve been using the information provided by the lab as a starting point for my reconnaissance. The website gives us several employees and their email addresses, but none of them are identified as IT staff. I also found the DNS SOA contact (hostmaster.bartertown.bitnet), but that appears to be a standard administrative DNS alias rather than an actual employee. The mail server does not seem to allow useful anonymous user enumeration, and the other reconnaissance results have not revealed the missing user. Has anyone completed this lab and can give me a hint about where/how the missing target information is supposed to be discovered?77Views0likes1Comment