immersive labs application security
24 Topics
Snort Rules: Ep.9 – Exploit Kits
I am pulling my hair with question number 8 Create a Snort rule to detect the third GET request in the second PCAP file, then submit the token. This one should do it but it is not working. alert tcp any any -> any any (msg:"detect the third GET request"; content:"e31e6edb08bf0ae9fbb32210b24540b6fl"; sid:1000001) I tried so many rules base on the first GET header and still unable to get the token. Any tips?Solved401Views0likes3Comments
Advanced CTF Challenge: Serial Maze
Need hint on Serial Maze. Have gone through html & javascript, couldn't find the token. Using dirb found one endpoint "http://10.102.17.87/2257", its response "What a pickle... You need the secret to continue." No sure how to proceed form here. Thanks, SabilSolved330Views0likes3CommentsIntroduction to Elastic: Ep.9 - ES|QL
I’m stuck on question 18 i need this to complete the lab. The question says ‘Perform a final query using all of the techniques used in the previous questions. What is the average speed per hour for ALL trips that start in the borough of “Brooklyn” and end in the borough of “Manhattan”? Provide your answer to at least three decimal places. any ideas?Solved300Views1like1Comment
Modern Encryption Issue
I'm on the last training under Modern Encryption training. I'm getting this error: ─$ openssl enc -des-ede3-cbc -d -pbkdf2 -nosalt -in encrypted_file_3DES.enc -out DES3 enter des-ede3-cbc decryption password: bad decrypt 139655774025024:error:06065064:digital envelope routines:EVP_DecryptFinal_ex:bad decrypt:../crypto/evp/evp_enc.c:610: The key is in text file from previous steps. I'm on step #7. I used the same syntax for decryption as earlier in this series. I tried various things, but still getting this error. I added the -a switch as well.Solved299Views0likes11Comments
Trick or Treat on Specter Street: Morphy's Mansion Challenge
I understand that the move_logger is the vulnerable program, and tried a few methods to exploit it. However, where is the token.txt? Anyone managed to find it? "Whatever means necessary" is quite broad. Any hints from anyone?Solved200Views0likes1CommentCVE-2022-26134 (Confluence) – OGNL Injection
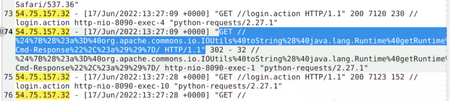
For Question 6. Look at the first exploit attempt by this attacker. What command did they run? I am wondering about why when sharing the commands found in the logs, it still outputs wrong. even if typing in "X-Cmd-Response" as the command as well as the entire string found. Wondering if they are exepecting a different format/snippet of the code, or the GET requests instead?103Views0likes4Comments
Abusing Trust Boundaries for RCE
I'm a bit stuck on this one as I'm not that familiar with Git and all the associated terminology. How do I clone the repo? which dir does the .mcp.json file sit in? Does this not pre-exist as its adding extra capabilities\extension to the original code? Does the target host pull the file automatically to give me a shell? Many thanks - GusSolved100Views0likes2CommentsNetwork Hardening Lab Recommendations
I've been looking for some good training resources for network hardening. I've been working through the Windows Hardening collection and found it really useful. Are there any other lab recommendations similar to this? In particular hardening things such as PfSense firewalls, Vyos routers, Linux endpoints etc.Solved100Views0likes3Comments