challenges
74 Topics
Tuoni 101: Demonstrate your skills Q3
I have successfully gained an initial foothold on Target 1 but am stuck trying to escalate privileges to the IT user. I have used jump-service to escalate to NT AUTHORITY\SYSTEM but this hasn't completed the task. I have been trying different things for over a week now but nothing seems to work. Any advice would be appreciated.4Views0likes0CommentsAI Red Teaming: Initial Access – Supply Chain Attacks
Hello all, I'm trying to complete the final task for this challenge to obtain MERIDIAN_API_KEY. I was able to get the API admin token. I see the information on the /env page that I'm supposed to access it through API. I'm trying to create a curl query - but I fail. I feel like it's a wrong direction.😟 Am I going the right way, or I should consider, check something. Any high level hints are appreciated.6Views0likes0Comments
DFIR CTF: LightNeuron DLL - Question 8
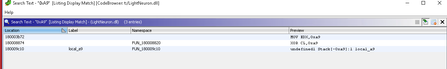
In relation towards finding the decrypted email. I am wondering about what I am getting wrong from the conditional breakpoint in order to expose all the decrypted strings after the return function After searching up the XOR key location I went to from Ghidra Through the RET function which I thought would expose the strings I ran going to the ret function then after following the process in order to go to the DLL malware and got into the ret function I set the breakpoint and debug restarted However, it kept saying memory address unavailable. such as this also includes setting the CF flag to 0 I am wondering about what I am doing wrong here and where should I dig deeper? Note: used Gemini to help look into possible solutions however, refered to https://www.youtube.com/watch?v=Tc8Wl37uwYc for aid I have also tried to run to the function but for some reason it the instruction keeps catching it and making a return away from the malware by setting breakpoint towards there but I keep getting lost on how I could actually breakdown the return and evasion techniques. Wondering where should I be digging more to learn how to investigate this process despite the amount of returns stopping the function7Views0likes0Comments
FIN7 Threat Hunting with Splunk: Execution Analysis
Hello everyone, I am stuck at the following task : "Which IP address and port does the encrypted payload communicate with? (Format ip:port)" I think I found the right function (babymetal) as I could answer the previous question : "What key is used to decode the embedded shellcode?" But where do I go from there ? I thought about doing dynamic analysis, but I have no tools to do so. Quite frankly I am lost Thanks for your help143Views0likes2Comments
AI Foundations: Retrieval Augmented Generation (RAG) Lab
Within step 6, the instruction says after creating the Knowledge base "My Intellectual Property" folder, xto change the chuck size to 65 however a Warn is displayed saying, "Please add both embedding model and LLM in the setting>Model provider fist. then set them in the "set default models'. After selecting the Ok button, I try to add vai the Set default model but then see this... "The default embedding model for each newly created knowledge base. If you cannot find an embedding model from the dropdown, check if you are using RAGFlow slim edition (which does not include embedding models) or check https://ragflow.io/docs/dev/supported_models to see if your model provider supports this model." Not sure how to address/resolve, any assistance will be helpful. Thank you, Tony75Views0likes1Comment
Struggling to find the IT email on Simulations: BarterTown Delivery
During the last few days, I’ve been stuck on this lab, and I’m not sure what I’m missing. The lab asks us to use OSINT tools and techniques to gather intelligence about individuals to target within the organization, with the goal of testing the awareness of BarterTown’s IT staff and eventually gaining a foothold in the internal network. I’ve been using the information provided by the lab as a starting point for my reconnaissance. The website gives us several employees and their email addresses, but none of them are identified as IT staff. I also found the DNS SOA contact (hostmaster.bartertown.bitnet), but that appears to be a standard administrative DNS alias rather than an actual employee. The mail server does not seem to allow useful anonymous user enumeration, and the other reconnaissance results have not revealed the missing user. Has anyone completed this lab and can give me a hint about where/how the missing target information is supposed to be discovered?78Views0likes1CommentThreat Research: Dependency Confusion exercise 8
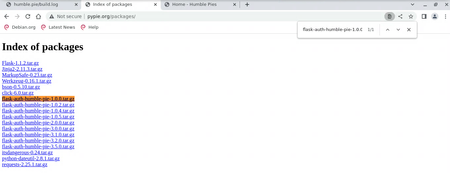
Humble Pie is not updating after 60 seconds it is stuck in the version 1.0.0 my packages have been created my setup.py seems to be working fine But I am never getting an answer in listening, never getting the connection and build.log is NEVER updating to latest version why is this not working... I really need to have this lab finished for my work.68Views0likes1CommentExercise "Web Server Brute Force Authentication: Anti-CSRF Tokens" broken?
Is this training really working? Every interaction with the page "Immersive Airport Display Management Systems" displays "csrf token is invalid". From the briefing it sounds all doable, do a get, get the token, send it in the post in a loop with the passwords. But it doesn't work for me at all.86Views0likes1Comment